Evaluating Manual and Tiered SEO Strategies
Quickly switch in between your cards, banks, crypto wallets, and buy now, pay later on across gadgets, internet browsers, or AI representatives.
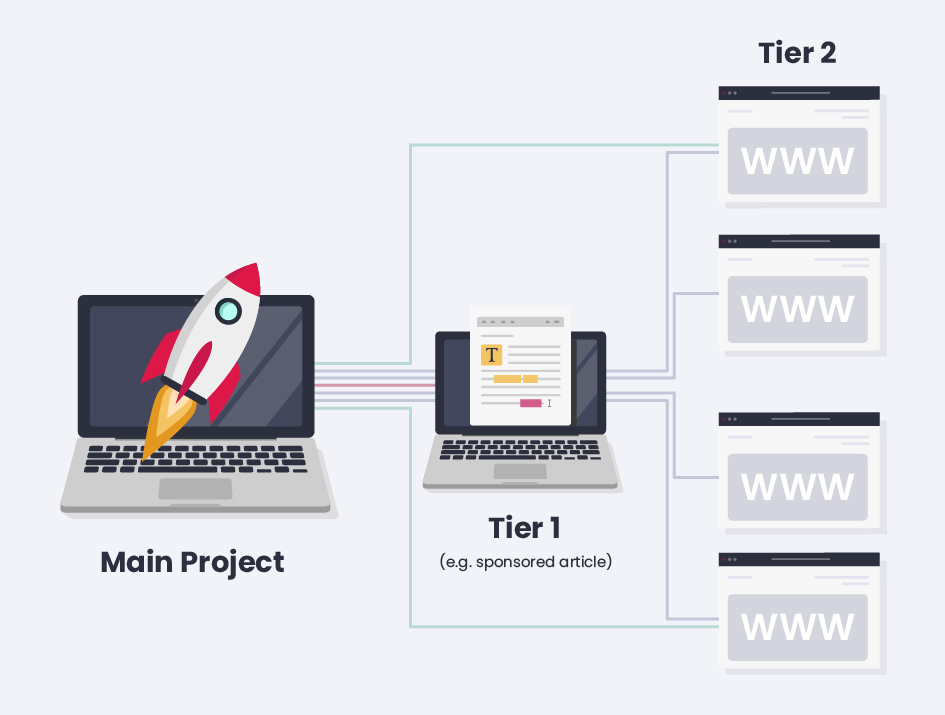
GSA SER tier 1 tier 2 tier 3
Discover relevant posts and skilled insights curated by subject and in one location. Link with buyers who have first-hand experience to find the finest items for you.
There are a number of other common types you'll come across. The sizes attribute shows the icon size, while the type contains the MIME type of the resource being linked.
Standard Methods for Managing GSA SER Campaigns
When using to establish a favicon for a website, and your site uses a Material Security Policy (CSP) to improve its security, the policy uses to the favicon.
Under XHTML 1.0, void components such as need a tracking slash: . WebTV supports making use of the worth next for rel to preload the next page in a file series. This aspect consists of the global attributes. This quality is needed when rel=" preload" has been set on the element, optional when rel=" modulepreload" has been set, and otherwise must not be used.
Moreover, rel=" preload" uses this as a signal for request prioritization. The table listed below lists the legitimate values for this attribute and the aspects or resources they apply to. As value Rel value Applies To audioworklet modulepreload AudioWorklet modules bring preload fetch, XHR This worth likewise needs to consist of the crossorigin quality, see CORS-enabled brings.
It should just be used when the rel quality consists of the expect or stylesheet keywords. With rel=" anticipate", it suggests that operations must be blocked up until a specific DOM node has been parsed. With rel=" stylesheet", it indicates that operations ought to be blocked till an external stylesheet and its vital subresources have actually been fetched and applied to the document.
Presently there is only one token: render: The making of material on the screen is obstructed. HTTP header) is carried out, but no credential is sent (i.e., no cookie, X. 509 certificate, or HTTP Standard authentication). HTTP header) the resource will be polluted and its usage restricted.
If the server does not give credentials to the origin website (through Access-Control-Allow-Credentials HTTP header), the resource will be tainted and its usage limited. If the attribute is not present, the resource is brought without a CORS demand (i.e., without sending out the Origin HTTP header), avoiding its non-tainted usage. If invalid, it is handled as if the identified keyword was used.